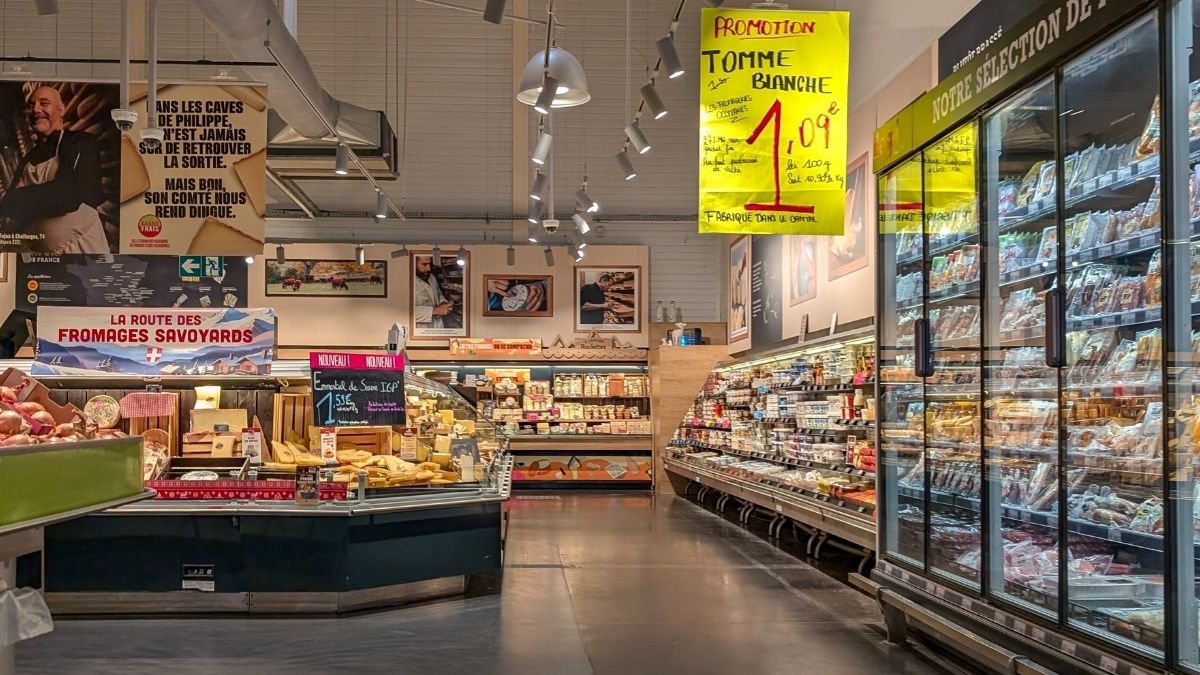
A widespread cyberattack targeting commercial refrigeration systems has forced hundreds of supermarkets across Europe to discard large quantities of refrigerated and frozen food. The incident, which occurred overnight between October 11 and 12, 2026, affected major retail chains including Intermarché, Netto, Carrefour, E.Leclerc, Monoprix, and Cooperative U. While the impact was most severe in France, reports indicate that retailers in Belgium, Germany, the Netherlands, Poland, Portugal, and Spain also experienced disruptions.
The attackers gained remote access to refrigeration controllers manufactured by the Danish firm Danfoss. By manipulating these systems, the perpetrators extended defrost cycles from one hour to eight hours and set target temperatures as high as 50°C (122°F). This interference delayed automated alarms, preventing store staff from intervening before the stock was ruined. Employees arriving at work reported being met with waves of hot air when opening freezers, and some locations experienced equipment damage and reports of fires.
Danfoss stated that the affected hardware primarily consisted of legacy products, specifically identifying the AK-SM800 and AK-SC355 systems, which no longer receive security or software updates. The company noted that it had previously advised customers to transition away from these obsolete models and maintain current firmware on supported equipment. The attack follows a disclosure by cybersecurity firm Claroty two months prior regarding vulnerabilities in the Danfoss AK-SM 800A platform that could allow for remote code execution and unauthorized configuration changes, though it remains unconfirmed if these specific flaws were exploited in this incident.
The financial impact of the attack is estimated to reach millions of euros, with the Paris prosecutor’s office opening an investigation into the incident. Retailers have been forced to withdraw products from sale where storage conditions could not be guaranteed, leading to temporary store closures and gaps on shelves. France’s national cybersecurity incident response center, CERT-FR, has issued guidance for operators, recommending that they restrict network access, perform factory resets, and apply all available security patches to their refrigeration management systems.
While the retailer Ahold Delhaize also reported a security incident around the same time that forced it to take systems offline, no evidence currently links that event to the refrigeration attack. The incident highlights the operational risks associated with connected industrial equipment, as the damage extended beyond digital systems to physical inventory and infrastructure. Recovery efforts are ongoing, with many retailers working alongside refrigeration specialists to restore normal operations and verify the safety of their remaining stock.